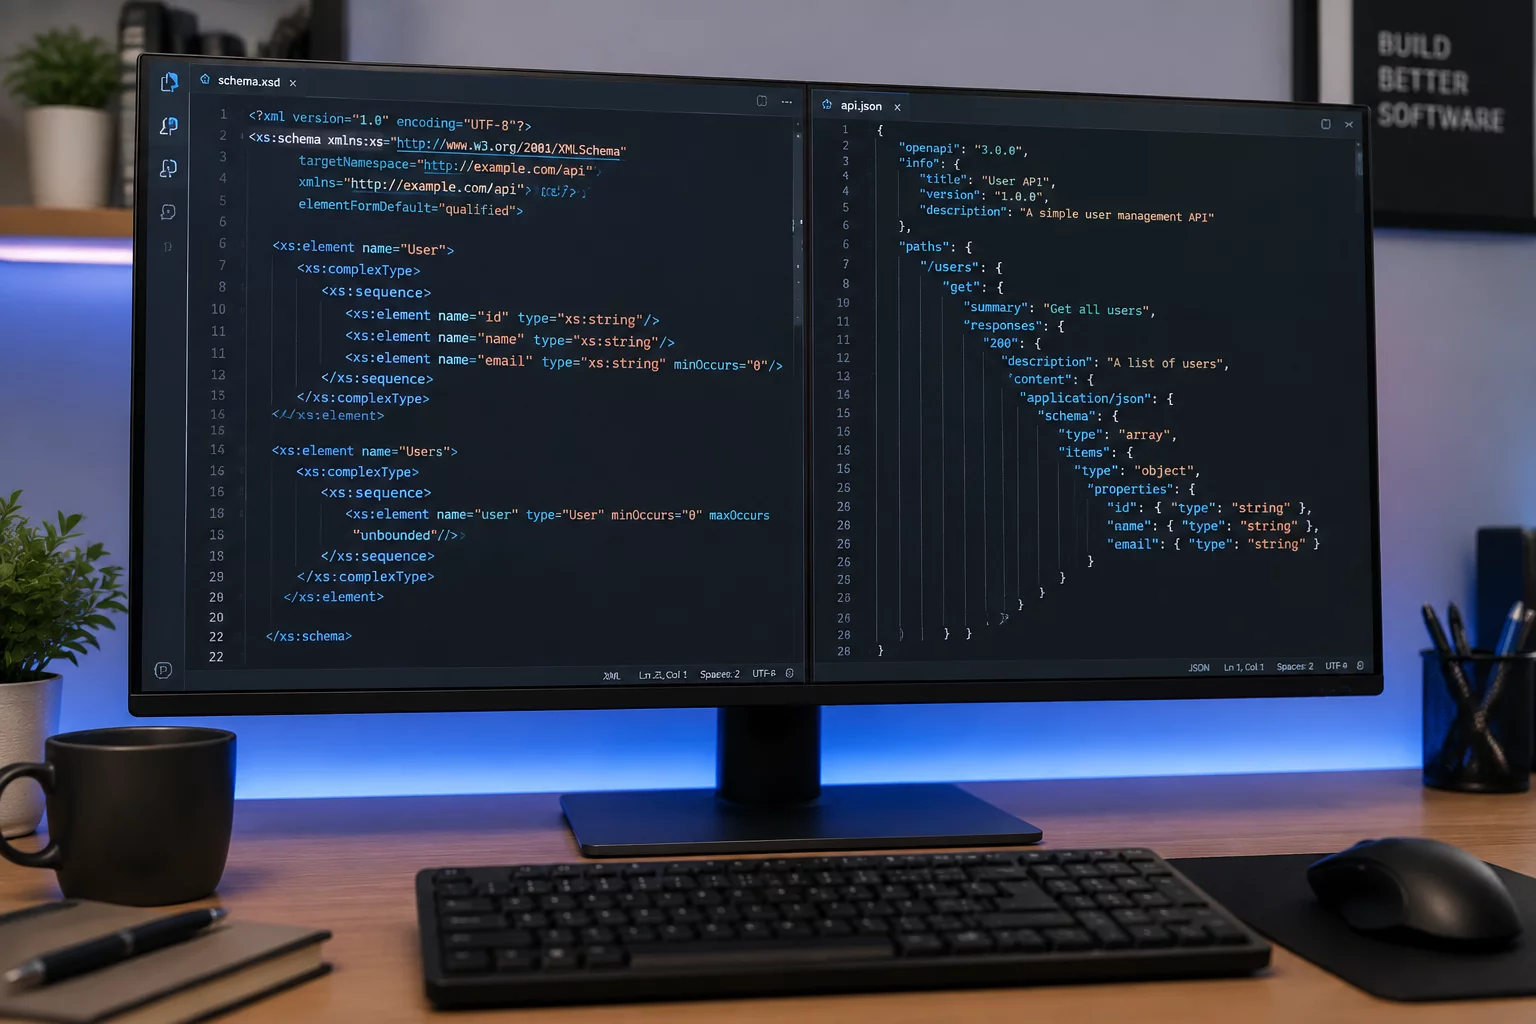
Architecture Shift: Legacy XML vs. OAuth 2.0 REST
For over two decades, the United States Postal Service operated its Web Tools API ecosystem on legacy HTTP endpoints that embedded user credentials directly within XML query parameters. Systems dispatching requests to endpoints like Secure.ShippingAPIs.com submitted plain identification tags inside AddressValidateRequest envelopes. While functional for lower transaction volumes in earlier web eras, this pattern created notable security exposure, lacked granular token scoping, and failed to meet modern zero-trust enterprise requirements.
The modernization initiative completely supersedes this legacy infrastructure with the USPS Developer Portal REST APIs secured by standard OAuth 2.0 client credential grants. Integrations now require programmatic client key and secret exchange against an authentication gateway, receiving short-lived JSON Web Tokens valid for 3600 seconds. This structural transition deprecates older protocol adapters and eliminates ad-hoc XML string parsing across warehouse management systems, legacy shipping consoles, and e-commerce checkout flows.
Field Mapping & Observed Protocol Differences
Moving from XML tags to RFC-compliant REST endpoints alters both transport headers and the internal representation of normalized delivery point attributes. The table below outlines how fundamental record fields transition between the retired legacy framework and the active REST API specification.
| Record Attribute | Observed State | Ledger Rule |
|---|---|---|
| Authentication Mechanism | Static USERID parameter in XML body | Authorization: Bearer {token} via OAuth 2.0 |
| Payload Serialization | Custom XML document with nested tags | Strict application/json request and response |
| Deliverability Status | Implicit inside ReturnText and DPVConfirmation | Explicit deliveryPointValidation object & flags |
| Rate Limiting & Quota | Undocumented server throttling / HTTP 500 | Standard 429 status code with Retry-After header |
Token Lifecycle & Verification Pipeline Risks
In high-throughput shipping and fulfillment pipelines, introducing OAuth 2.0 token management introduces potential failure modes if asynchronous token caches are improperly architected. When thousands of addresses are verified concurrently during peak fulfillment windows, requesting a new access token for every validation call rapidly exhausts rate quotas and introduces multi-second latency spikes.
Address verification pipelines must treat OAuth tokens as shared, thread-safe application state with proactive background renewal before the 3600-second expiration threshold.
Beyond token lifecycle management, engineering teams frequently overlook error schema discrepancies. Where Web Tools returned HTTP 200 containing an XML Error node detailing missing secondary unit designators or invalid ZIP codes, the modern REST platform returns RFC 7807 compliant HTTP 400 or HTTP 422 error structures. Without explicit schema mapping in upstream validation services, these errors trigger unhandled exceptions, stalling customer address normalization queues.
Migration Playbook for Production Systems
Transitioning legacy address validation logic to the OAuth 2.0 REST endpoints requires a methodical, step-by-step decoupling process to prevent shipping disruptions and erroneous address alterations:
- Deploy an abstracted proxy layer that intercepts legacy XML queries and converts them to authenticated JSON requests before reaching the postal gateway.
- Implement centralized token caching with automated pre-expiry refresh buffers (refreshing at 50 minutes of the 60-minute token life) across distributed microservices.
- Execute dual-run shadow validation across production records to verify that postal normalization matches historical DPV outputs without unintended street name truncation.